User Management
Overview
Various aspects of the Custody Infrastructure solution need to be accessed by different individuals within your organization.
To effectively manage user permissions and access, consider the following:
- Assigning Roles:
- Users should be assigned specific roles based on their responsibilities and required access levels. Roles define what actions a user can perform within the system.
- By assigning roles, you ensure that each user has appropriate permissions without granting unnecessary privileges.
- Utilizing Groups:
- Groups are valuable for managing multiple users collectively. Instead of configuring permissions individually for each user, you can organize them into logical groups.
- Group-based management streamlines administration and ensures consistent permissions across team members.
Only an administrator can create and manage users, user groups, and roles.
Users must be added to the system before they can be managed. See:
- Adding a Local UserAdding a Local User
- Adding and Registering a Remote UserAdding and Registering a Remote User
Creating Roles
Log in to the cold vault.
Go to the User Management page.
Click + Add new role.
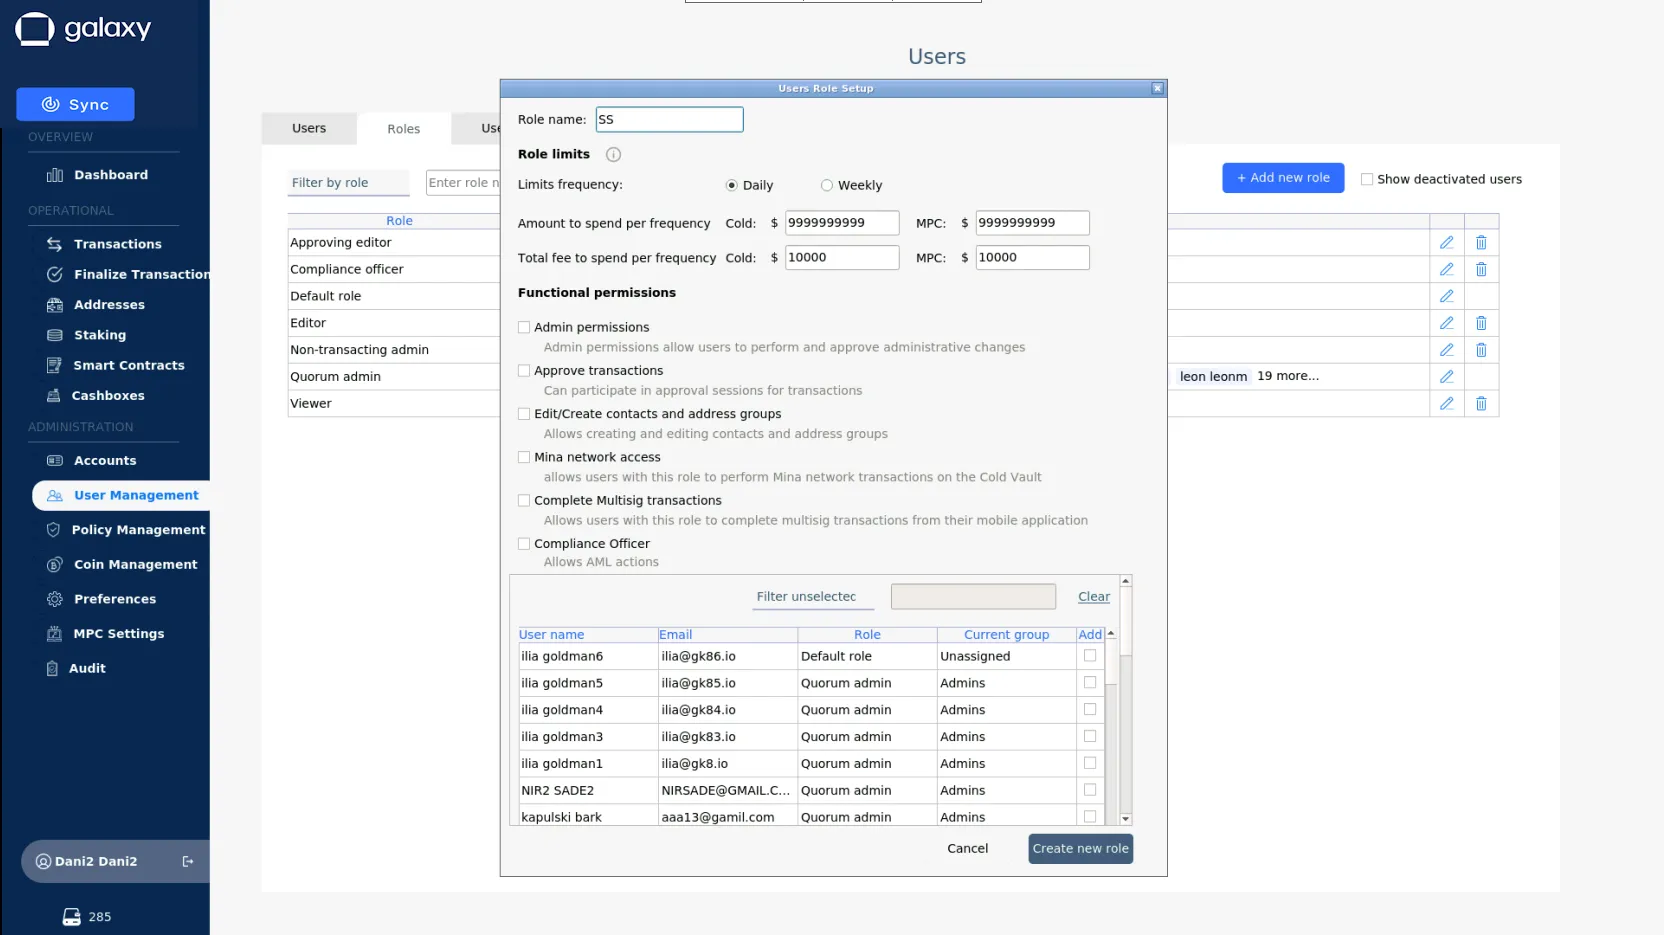
Name the new role.
Configure the Daily/Weekly limits for the role.
The limits are cumulative, not per transaction. The daily limit is a rolling window encompassing the last 24 hours. The weekly limit counts the last seven days' total transactions.
Assign Functional Permissions by ticking the respective checkbox:
- Admin Permissions - allows to perform admin changes to that role
- Approve Transaction - allows the user to approve any transaction. System policies can be used to limit what transactions a specific approver is capable of approving.
- Edit/Create contacts and address groups
- Other network-specific permissions according to the need.
- From the role definition set you can choose a specific user to move to that role.
Click Create new role. The role is saved.
Adding a User to a Group
Groups are typically aligned with specific organizational departments, such as management, finance, or information security. They help organize users based on their roles and responsibilities. Additionally, a group can represent a collection of users who share common viewing permissions or participate in a unified workflow approval process.
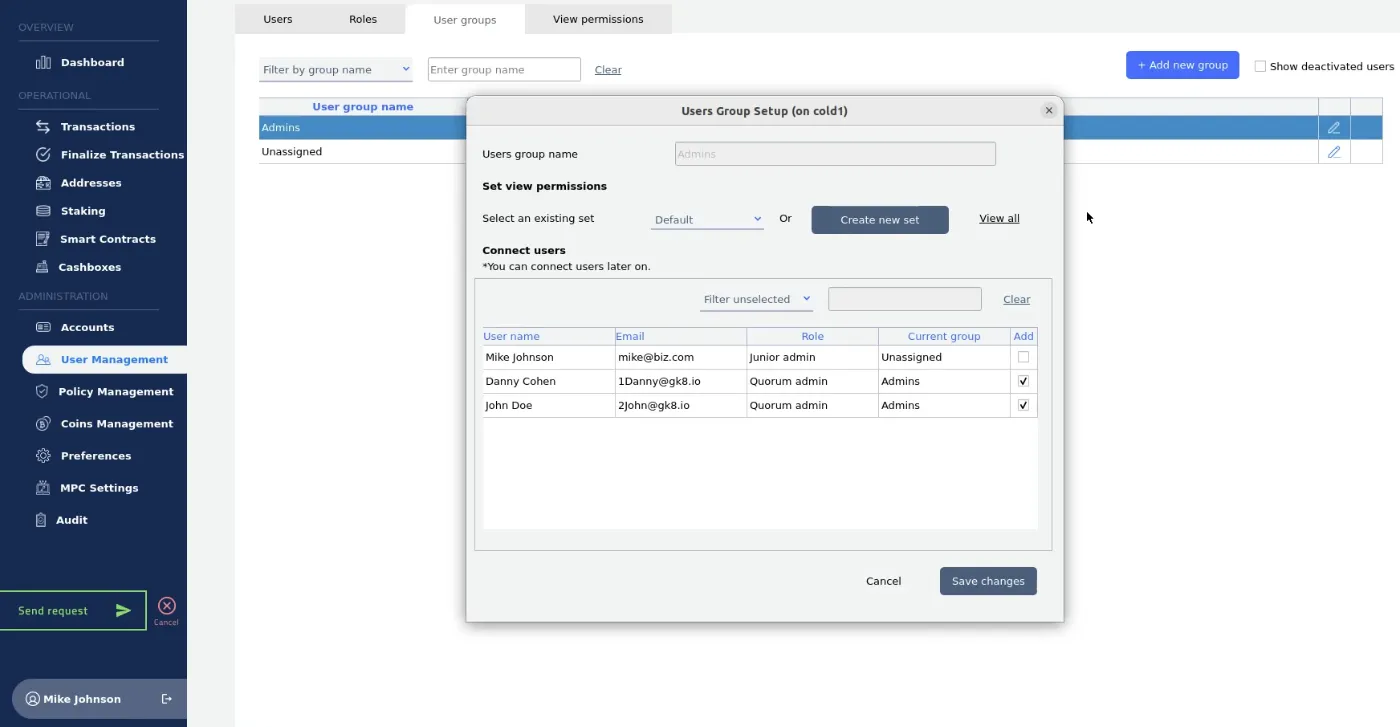
To set the policy for a specific user, open the User Group Manager tab and choose a specific user to connect to a specific group.
Before adding a user to an admin group, make sure they have admin permissions in their current role.
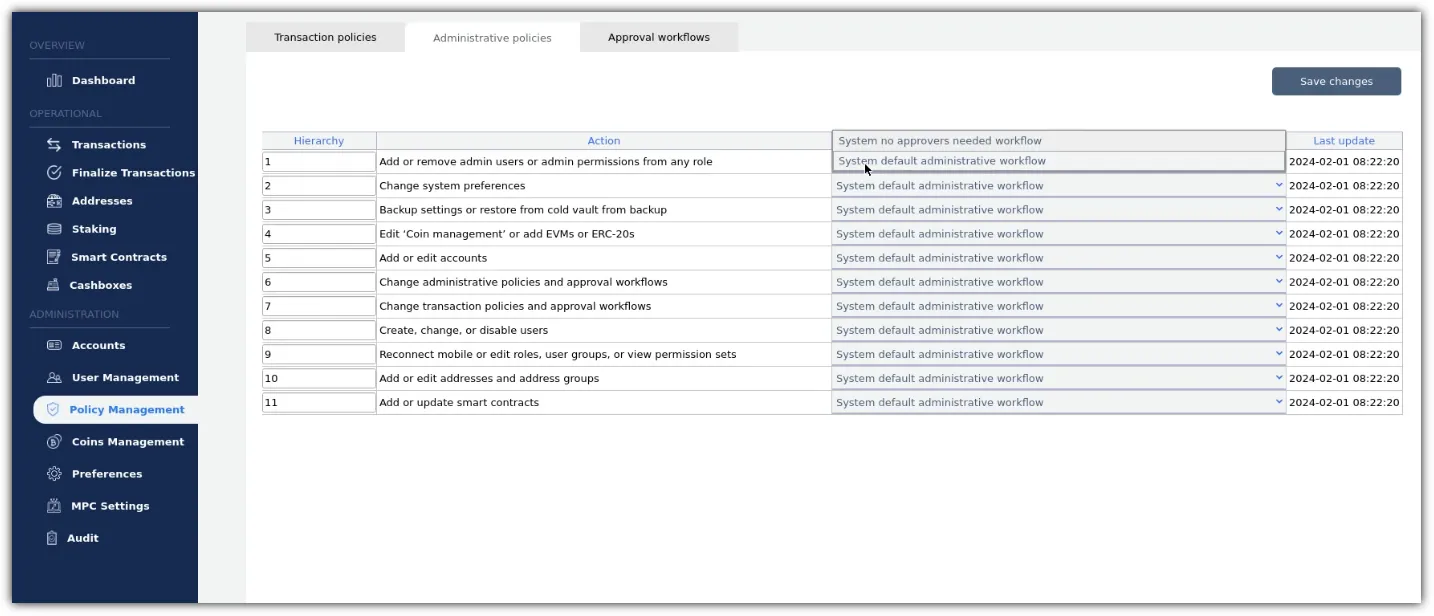
The process of approving user additions to a group relies on the approval workflow associated with a specific Administrative Policy.
To review the current approval workflow:
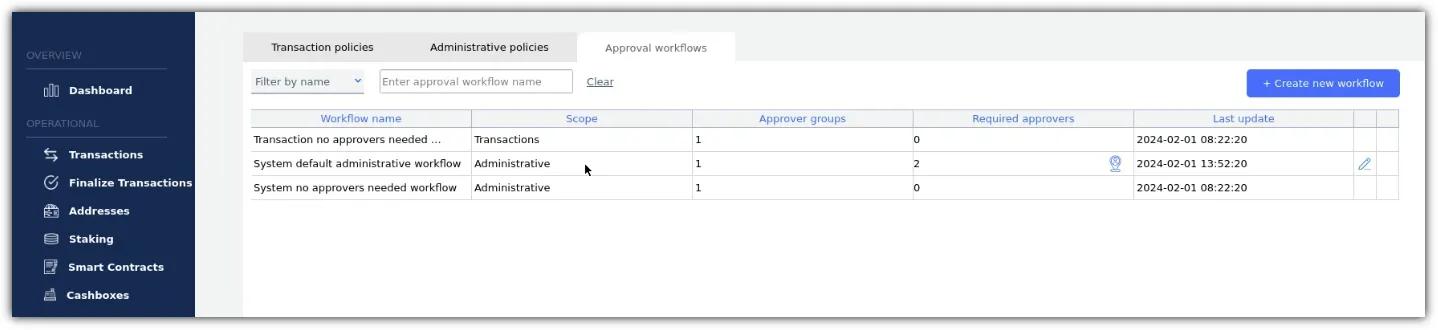
Navigate to the Approval Workflow tab.
Review the workflows list.
Go to the Administrative Changes tab and check which Approval workflow is assigned to this type of change.
To determine the number of available and required approvers for this type of change set with the System Default workflow, examine the workflow settings.
Submit the approval request and complete the process with the required approvers.