Policy Management
The policy management area is where you configure Transaction and Administrative Policies and define Approval workflows.
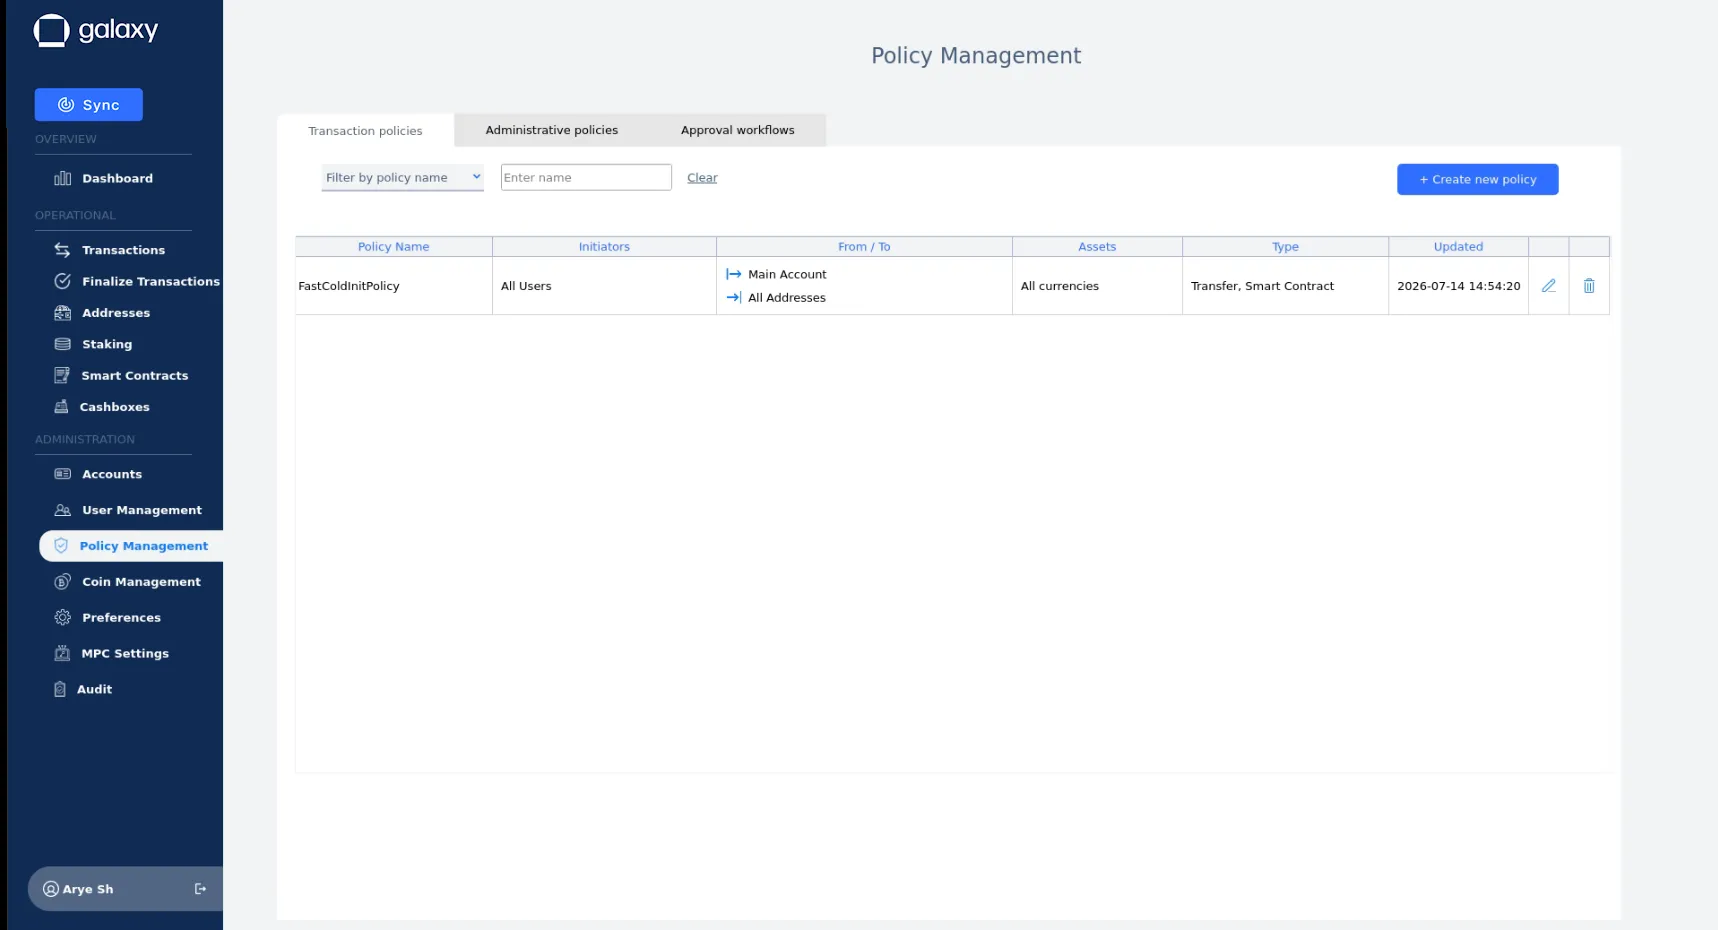
Transaction Policies
Transaction policies enable organizations to enforce strict oversight and control over outgoing transactions. Any time a user creates a request, the system checks the proposed action against the criteria listed here:
- Who creates transaction requests and who approves them.
- From/To where accounts funds can be sent and to which destinations.
- How much can be transferred.
- Which assets over which blockchains and in which currencies.
- Which types of blockchain interactions are allowed (for protocols that allow multiple types of interactions).
- If approval is required and by whom.
If there is a policy that corresponds to the requested transaction, the system goes through the action configured in the policy's approval workflowsapproval workflows.
Transaction Policy Types
Transaction Policies come in eight types, briefly outlined below:
- General Transfer: Governs asset transfers from one address to any other another. Policy covers transfers originating from addresses within the Custody Infrastructure system, whether those transfers are destined for another address within your system, or to an external destination.
- Internal Transfer: Specifically governs asset transfers from addresses within the Custody Infrastructure system to another address within your system. For example, moving assests from one account to another or from the Impenetrable Vault to the Galaxy Custody Desktop app.
- Staking: Enforces rules for staking assets. Assets can only be staked to validator addresses.
- Signature type: This option covers smart contract transactions (other than deployment). There are two options, either or both of which can be chosen for the same policy.
- Personal Sign: Personal signing allows you to confirm ownership of data but cannot be used to transfer assets.
- EIP-712 sign: This is required for policies dealing with dapps. It is the safer and more structured signing option.
- Tokenization: Manages interactions with smart contracts, ensuring compliance with operational rules.
- Deploy: This policy option covers designated users deploying smart contracts from specified accounts.
- Raw Signing: Controls operations that involve signing raw data.
- Canton Topology: For transactions that relate to the Canton coin.
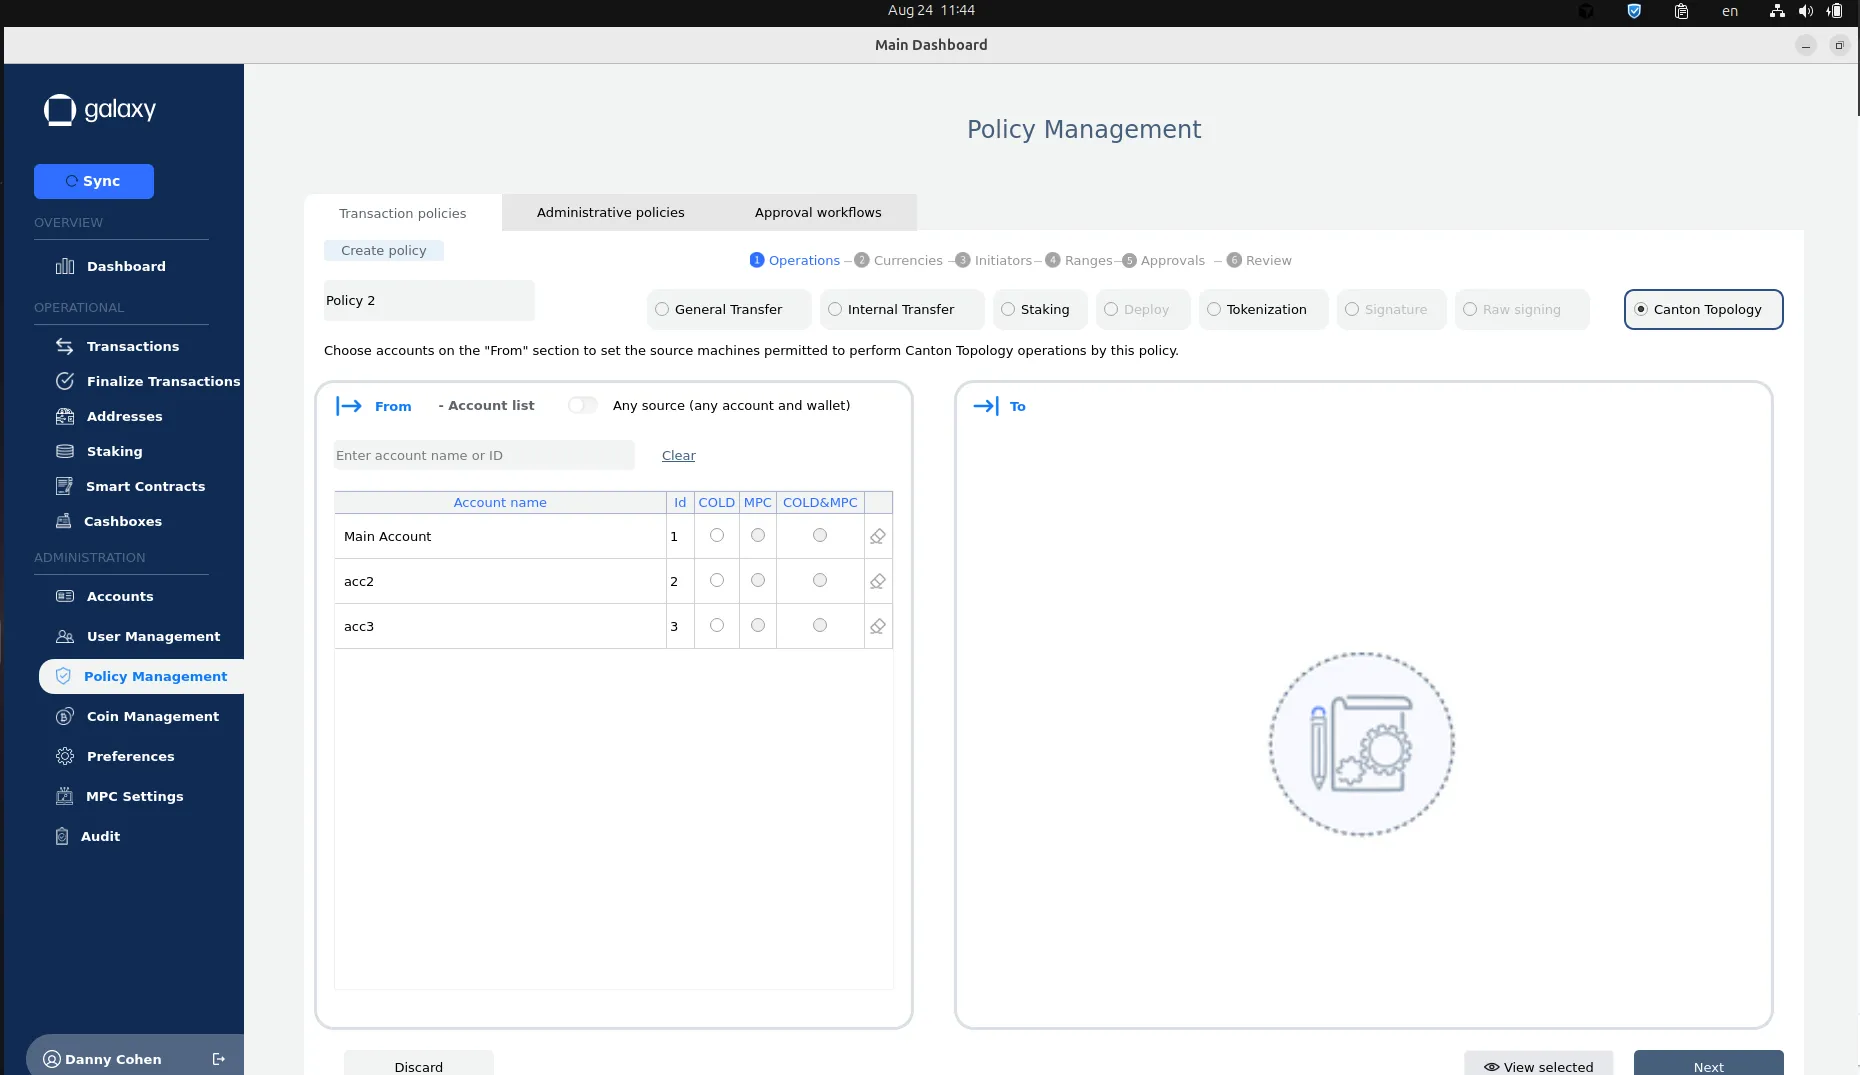
While each type of transaction policy covers a different scenario, they all share the same configuration process, covered in detail in Create Transaction PoliciesCreate Transaction Policies.
Before certain elements can be added to a policy, they must first exist as entities in the system. These entities include:
- Approval Workflows: Which approvers need to confirm transactions is configured in the Approval Workflow management area.
- Contacts: Both ordinary contacts and validator addresses need to be in the address book before they can be added to a policy. See Addresses management for more information.
- Roles: Different approval flows can be required depending on the initiators' roles. See User Management.
- Users/User Groups: These must exist before they can be added to a policy. User groups can be used to add new users to a policy at any time, just by adding the user to the included user group. See User Management for details.
For more details, see:
- Transaction Policy creation and managementTransaction Policy management
- Administrative Policy managementAdministrative Policy management
- Approval Workflow managementApproval Workflow management